Connect Token Saver to your AI host
Choose your harness for exact setup, OAuth, verification, and host instructions, then run the complete tier-first lifecycle.
https://tryelisai.com/mcp, wait for it to report ready, and retry.Choose your harness
Each tab is a complete setup path and has a shareable ?harness=... URL. Do not substitute one harness's endpoint or configuration keys for another.
Antigravity setup
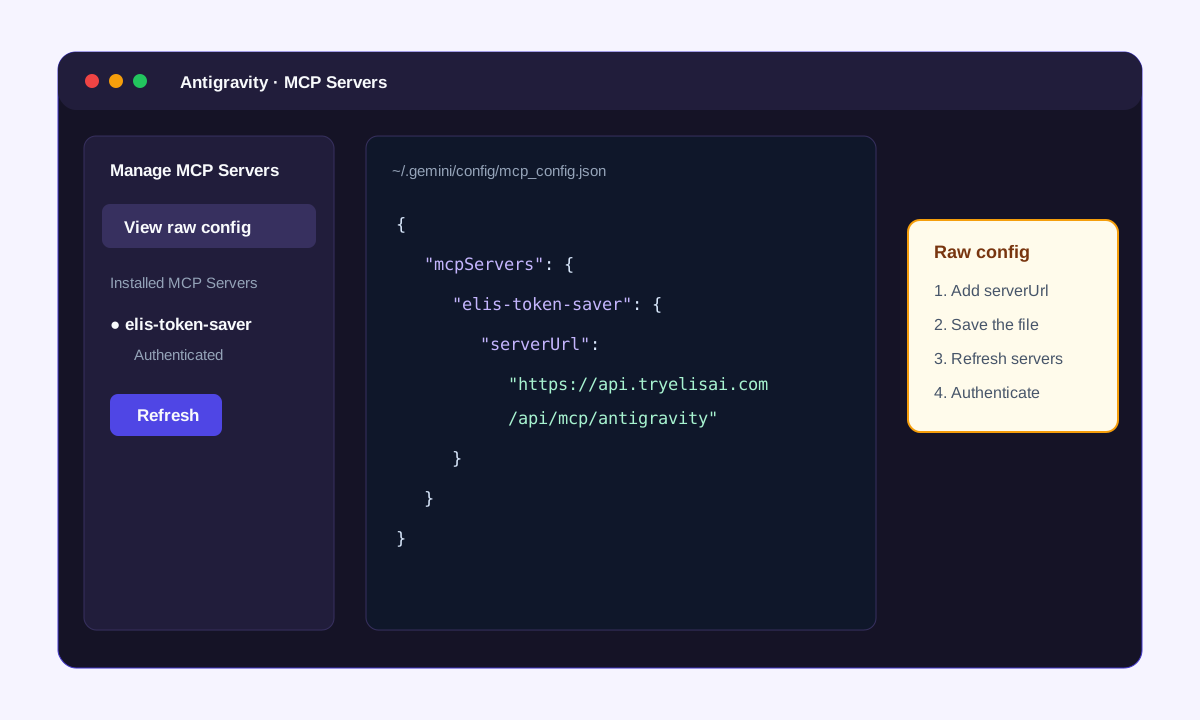
Antigravity supports local and remote MCP servers. Its IDE and CLI share the active MCP configuration.
1. Open the configuration
Agent panel → … → MCP Servers → Manage MCP Servers → View raw config. The active file is normally ~/.gemini/config/mcp_config.json.
2. Add Elis Token Saver
{
  "mcpServers": {
    "elis-token-saver": {
      "serverUrl": "https://api.tryelisai.com/api/mcp/antigravity"
    }
  }
}
3. Authorize
- Save the raw configuration, return to Installed MCP Servers, and refresh the list.
- Choose Authenticate if the server requests OAuth, then complete the Elis browser consent flow. If your Antigravity build does not expose that action, use the programmatic PKCE flow below.
4. Verify the connection
- Confirm elis-token-saver appears in Installed MCP Servers without an authentication warning.
- In the Antigravity CLI, /mcp should list the server as authenticated and expose its lifecycle tools.
5. Install the host behavior
.agents/rules/elis.md
.agents/agents/elis.md
Antigravity Customizations → Workflows (manual install)
setup_elis_host_instructions previews the rule and executor files. It returns the /elis workflow as a manual installation because Antigravity does not document a stable workspace workflow-file path.
Endpoint: https://api.tryelisai.com/api/mcp/antigravity
References: Google: Antigravity MCP configuration · Complete Elis setup reference
Run the complete Elis lifecycle
Connecting the server only exposes tools. The host must still use the same cursor for the whole plan and execute only the tasks Elis discloses. Every ready task includes an authoritative recommended_model_size of nano, small, or frontier. A named model is optional host guidance, not a hardcoded binding.
1. start_elis_token_saver_plan({ goal, constraints?, chain_hint? })
2. submit_elis_task_plan({ plan_id, tasks })       // only when start requests it
3. get_next_elis_task({ plan_id, graph_revision })
4. Execute every ready task using its public execution_handoff and size tier
5. get_next_elis_task({
     plan_id,
     graph_revision,
     previous_result: { task_id, status, output },
     usage: { input_tokens, output_tokens, model, model_tier }
   })
6. Repeat steps 4-5; switch immediately if the server returns a new graph_revision
7. finish_elis_plan({ plan_id, final_answer, total_tokens_used, usage, feedback })execution_handoff, completes that one task, reports actual model and token usage, and returns control. It does not start a second plan.Authorize a host without built-in OAuth
A raw JSON-RPC client must implement OAuth itself. First read public discovery metadata, register a public client, create an S256 PKCE challenge and state, open consent, validate the returned state, exchange the one-time code, and send the access token in the header.
Show the programmatic OAuth checklist
- Read
https://api.tryelisai.com/.well-known/oauth-authorization-server. - POST
{"client_name":"my-host","redirect_uris":["http://localhost:8765/callback"]}tohttps://api.tryelisai.com/oauth/registerand retain the returned publicclient_id. - Generate a random
code_verifier, its base64url SHA-256code_challengewithout padding, and a randomstate. - Open
/oauth/authorizewithresponse_type=code, the exact redirect URI,code_challenge_method=S256, scopeprofile token_saver, the state, and the selected harness endpoint asresource. - Verify state, then POST the code, client id, verifier, exact redirect URI, resource, and
grant_type=authorization_codeto/oauth/token. - Call the selected MCP endpoint with
Authorization: Bearer <access_token>. Keep tokens out of URLs and logs.
The copy-paste requests and refresh-token notes are in the full setup reference.
Use recall and privacy controls deliberately
A successful authenticated finish can store a proven chain privately in the selected Personal or organization scope. Future similar goals can recall that task sequence. Report honest ok, failed, or blocked task status and actual usage so prediction and savings audits compare against real execution.
// Do not store or recall this plan
start_elis_token_saver_plan({ goal, constraints: { no_store: true } })

// Keep private recall, but exclude this plan from community sharing
start_elis_token_saver_plan({ goal, constraints: { no_community: true } })

// Recall a known private proven chain for a similar goal
start_elis_token_saver_plan({ goal, chain_hint: "elis_chain:<sig>:<plan_id>" })Troubleshoot the common failures
- No tools: confirm the exact harness endpoint, Streamable HTTP config, host trust/enablement, and workspace MCP policy. Then refresh tools or restart the host.
- oauth_required or invalid_token: the server is reachable, but the lifecycle is not authorized. Complete authentication again; do not continue anonymously.
- insufficient_scope: authorize again with
token_saverin scope. - payment_method_required: open
https://app.tryelisai.com/billing, attach a payment method to the selected scope, then retry the lifecycle call. - First request times out: wake the API at
https://tryelisai.com/mcpand retry after it reports ready. - /elis missing: apply every file returned by
setup_elis_host_instructionsand start a new host session. Gemini CLI can reload commands with/commands reload. - Plan revision changed: stop work tied to the old
graph_revisionand follow the new ready-task wave.
For tool schemas, usage fields, tier semantics, grounding, and finish behavior, continue to MCP Tools & Tier-First Lifecycle.